Sample report
Read a complete sample penetration test report
This is the report a client receives at the end of an engagement, from the executive summary to the retest results. The client and the findings are fictional. The structure, the scoring and the level of detail are those of a real report.
Open the report
- Open the English version, opens in a new tab
PDF · 19 pages · 240 KB
- Open the Arabic version, opens in a new tab
PDF · 20 pages · 360 KB
No sign-up and no email address needed. The file opens in a new tab.
Example Trading Company does not exist. Its systems and the findings were written for this sample, and no client's data appears in it.
Pages from the report
 , opens in a new tab
Cover 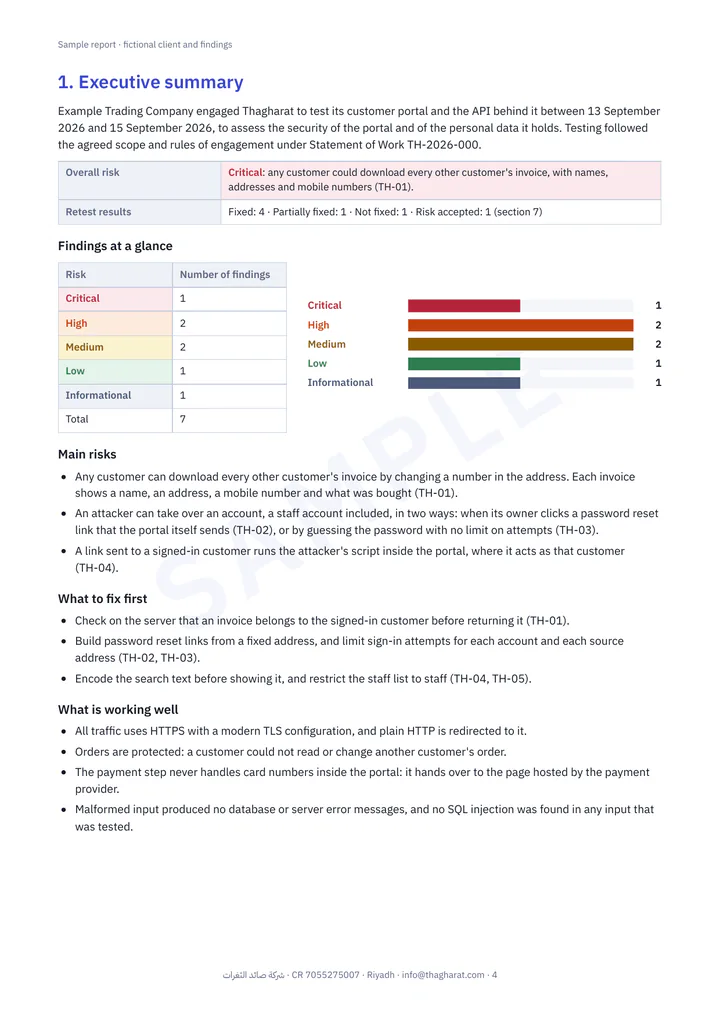 , opens in a new tab
Executive summary 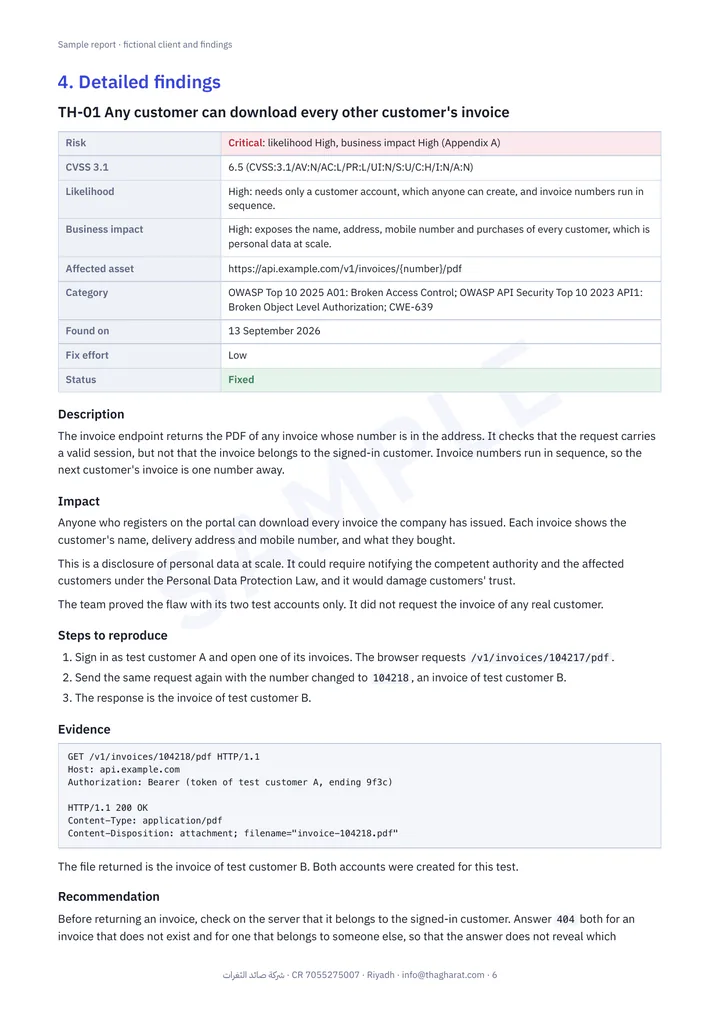 , opens in a new tab
A finding in detail
What is in the report
Executive summary
One page for leadership: the overall risk, the findings by risk level and what to fix first.
Seven findings in detail
From critical to informational. Each has its risk rating, CVSS score, evidence, steps to reproduce and a specific fix.
Remediation roadmap
The fixes grouped by priority, with a suggested timeframe for each group.
Compliance mapping
Each finding mapped to what it affects in the PDPL, NCA ECC and ISO 27001.
Retest results
The status of every finding after the retest: fixed, partially fixed, not fixed or risk accepted.
Scope, method and coverage
What was tested and how, how risk is rated and what the test covered in the OWASP WSTG.
Your report comes in Arabic, English or both, and one retest is included. See packages and prices.
Get started
Tell us what you need tested
A few lines on what you want tested are enough, with no sensitive detail at this stage. We will reply with a proposed scope, a timeline and a fixed price. There are no sales calls and no obligation, and we sign an NDA before you share any technical detail.
The fastest way to reach us. We aim to reply the same working day.
- NDA before any technical detail
- Fixed price for the agreed scope
- One retest included
How we handle your details: Privacy Policy